


Workspaces
Workspaces offer a multi-tenancy capability, enabling you to create multiple isolated instances in your Cribl.Cloud Organization. This lets you strengthen your security, and fulfill compliance and isolation requirements.
Each Workspace offers a dedicated virtual private cloud (VPC) that acts as a separate environment within your Organization. Workspaces do not share product configurations, resources, or data flows, and each has a separate Leader Node. They do share a layer of access control (Organization-level Permissions and SSO configuration), as well as API credentials, licenses, and billing.
A centralized interface allows you to manage all your Workspaces and control access for Members and Teams to individual Workspaces.
Multiple Workspaces require a Cribl.Cloud Enterprise plan.
An example use case scenario for creating multiple Workspaces is setting up separate environments for different business units in an enterprise. Data management, security, development, and any other units can have their own federated Workspaces, with completely separate Members and Permissions lists. This way, they can work in isolation without risk of interference and with increased focus.
Limitations
The number of included Workspaces depends on your Cribl.Cloud plan:
| Plan | Included Workspaces | Additional Workspaces you can add |
|---|---|---|
| Standard | 1 (the Main Workspace) | N/A |
| Enterprise | 3 | Up to 2, at 250 credits each per month |
On an Enterprise plan, Organization Owners and Admins can add Workspaces beyond the included allowance. When you have used the 3 included Workspaces, you can add up to two more on the Manage Workspaces page for 250 credits each per month.
When you select Add Workspace, Cribl.Cloud opens Accept additional cost? Select Accept to continue, or Cancel. The confirmation states that each Workspace you add costs an additional 250 credits per month, reflected in your next billing cycle.
Charges for additional Workspaces appear on your invoice under Infrastructure. See Understand Your Monthly Invoice.
In Cribl.Cloud, one credit equals one US dollar. An additional Workspace therefore costs $250 per month, prorated daily. See How Is Cost Calculated?.
Switch Workspaces
When you have access to multiple Workspaces in your Cribl.Cloud Organization, you can switch between them from the top bar in any Cribl product:
- On the top bar, select your current Workspace name.
- In the drop-down, select the Workspace you want to switch to.
The drop-down lists Manage Workspaces first. Select it to open the Workspace management modal, where you can add, edit, or delete Workspaces.
Below Manage Workspaces, the drop-down lists your Workspaces with the current Workspace first, followed by other Workspaces in alphabetical order.
If your Organization has only one Workspace, selecting the Workspace name on the top bar opens the Workspace management modal directly.
Manage Workspaces
To list the Workspaces in the Organization, in the sidebar, select Workspace or Organization and then Manage Workspaces. The list includes the name, ID, description, Cribl Insights retention status, tags, Cribl version number, and current state for each Workspace in the Organization.
Select a Workspace name or the ellipsis (...) in the Actions column to edit the Workspace name, description, and tags or delete the Workspace.
Release Channels
In Cribl.Cloud, Enterprise customers can assign each Workspace to the Regular or Slow release channel.
The Regular release channel (default) follows the standard monthly release cadence. The Slow release channel also updates on a monthly basis but is one version behind the Regular release channel. Cribl sends monthly notifications describing the versions published to each release channel.
Release channels give you self-service control over the upgrade cadence for each Workspace and allow you to validate new Cribl versions in pre-production Workspaces before deploying them to production environments. Release channel selection does not affect your support or product lifecycle.
Release channels determine when Cribl publishes feature and maintenance releases to Workspaces:
- Regular release channel (default): Cribl publishes new feature and maintenance releases to the Regular release channel monthly.
- Slow release channel: Cribl publishes new feature and maintenance releases to the Slow release channel one month after the corresponding Regular release enters production.
If Cribl publishes a hotfix to the Regular release channel within the previous two weeks, Cribl delays the Slow release channel update until the following month.
Cribl does not update the Slow release channel in November or December.
Cribl might deliver critical security and other emergency updates outside the normal release channel schedule. In these cases, to protect customer environments, Cribl might update Workspaces assigned to the Slow release channel to the same version as Workspaces assigned to the Regular release channel.
Change the Release Channel for an Existing Workspace
To change the release channel for an existing Workspace:
- On the top bar, select the current Workspace name, then select Manage Workspaces.
- Next to the Workspace that you want to update, select Settings in the Actions column.
- On the Details page, select the Release Channels tab.
- Select Regular or Slow.
- Select Save.
Cribl does not immediately change the Workspace version when you change its release channel. The Workspace stays on its current version until the next scheduled upgrade cycle.
Cribl does not downgrade a Workspace when you change it to the Slow release channel. Cribl does not support rolling back Workspaces to earlier versions.
For hybrid deployments, do not upgrade Worker Nodes in a customer-managed Worker Group or Edge Nodes to a version newer than the Leader Node version. For version compatibility requirements, see Supported Version Differences Between Leader and Workers and Supported Version Differences Between Leader and Edge Nodes.
View Workspace Details
Workspaces provide a set of information that you can use when configuring data flow through their Edge Nodes.
View Access Details
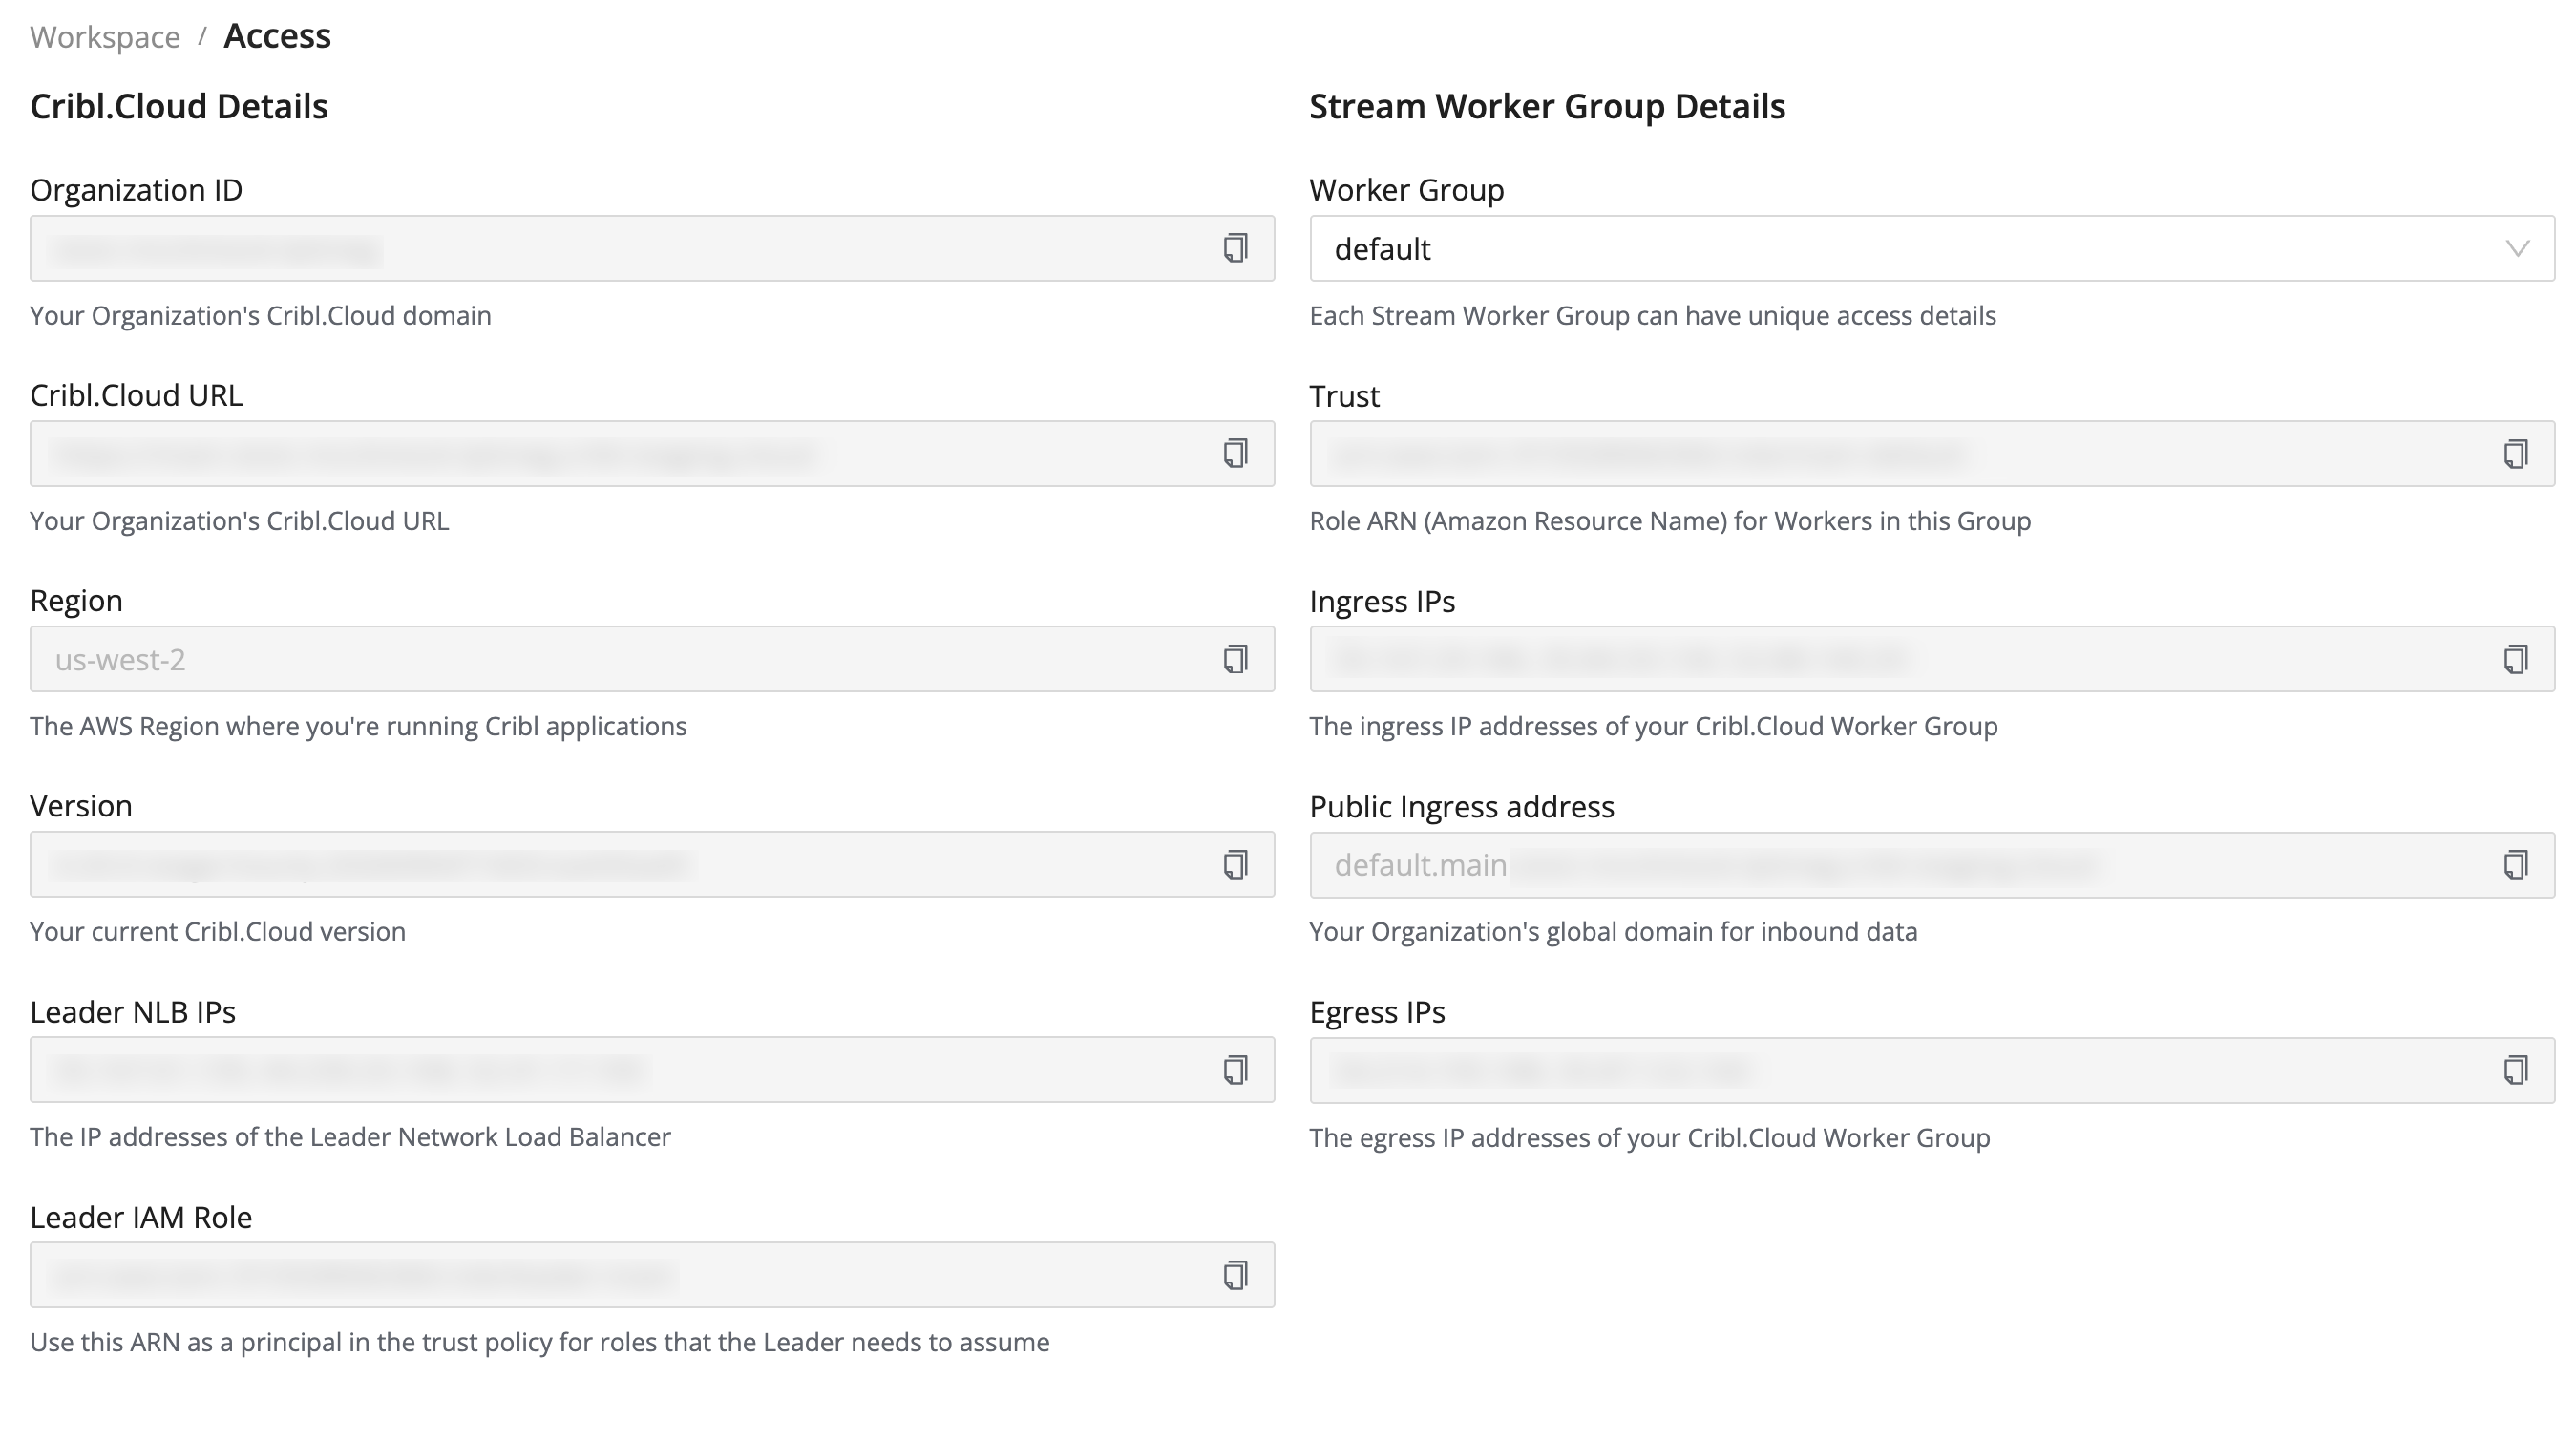
To view detailed access information of your Workspace, in the sidebar, select Workspace and then Access.
This page presents a summary of information about your Cribl.Cloud Organization, as well as the Cribl.Cloud URL for the current Workspace.
Cribl.Cloud URL
Cribl.Cloud URL is a static address associated with the load balancer that is in front of the Leader. Customer-managed (hybrid) Edge Nodes will connect to this address on port 4200, while the Leader UI is served from this address on port 443.
You can use this URL for certain API calls and certain Collection operations coordinated by the Leader.
Static External IPs for the Leader
The Leader NLB IPs field in Workspace > Access lists the IPs for the Leader Network Load Balancers associated with the Workspace.
Typically, only 2 of the 3 addresses will be active (returned by DNS) at any time, while the inactive address is swapped in during infrastructure maintenance events.
You can add all those IPs to your firewall allowlist to ensure that the load balancers are accessible across your hybrid deployment.
Stream Worker Group Details
Stream Worker Group Details provides information about Cribl-managed Worker Groups in Cribl.Cloud, if any are provisioned.
If no Worker Group is provisioned, you can select Provision Now to provision infrastructure for the Group. After a lag, the Group will be ready to process data, and this modal’s remaining fields will populate.
For a provisioned Worker Group, you see the following information:
| Field | Description |
|---|---|
| Trust | AWS IAM role ARN for Cribl-managed Workers in this Worker Group. On an AWS-based Worker Group, use this ARN as the principal in AWS trust policies when configuring cross-account access. Azure-based Worker Groups also display an ARN but do not have AWS credentials. The ARN in the Trust field is not usable in your AWS account. |
| Ingress IPs | The IPv4 addresses of Worker Groups’ load balancers, also used when receiving data from Push Sources. These addresses will remain constant, so you can build firewall rules around them. Three Ingress IPs are provided for each Worker Group, one on each Availability Zone, assuming the Group has at least three Workers. In a Worker Group of fewer than three Workers, one of the IPs will be inactive. |
| Public Ingress address | Each Group’s domain for inbound data. This address prepends the Group name to the Organization’s global domain name. It does not append ports per data type - you can obtain these from the Data Sources tab. |
| Egress IPs | The public IP addresses of your Cribl.Cloud Organization. These addresses are Group-specific. By default they are dynamic: Cribl will occasionally update them when we need to rescale core infrastructure. If you enable static egress for the region, these addresses stay stable so you can add them to firewall and Destination allowlists. |
Public Ingress address and Egress IPs are used for both outbound connections from the Workers and Pull Sources.
Because individual Ingress IPs can become inactive, Cribl recommends that you send your data to the Public Ingress address instead of directly to IPs.
By default, egress IPs are not static. To keep outbound traffic in a region on a stable set of IPs for Destination and firewall allowlists, enable Static Egress IP on Workspace > Connections.
Configuring Stream Groups (beyond the
defaultGroup) requires a certain plan. For details, see Pricing. For details about creating and provisioning Groups, see Cribl.Cloud Worker Groups.
View Data Sources
To view detailed access information about a Workspace’s Data Sources, in the sidebar, select Workspace and then Data Sources.
The Data Sources page lists ports, protocols, and data ingestion inputs that are open and available to use, including pre-enabled Sources. Use the Group drop-down to filter these details per Cribl-managed Worker Group in Cribl.Cloud. For details, see Available Ports and TLS Configurations.
For each existing Source listed here, Cribl recommends using the preconfigured endpoint and port to send data into Cribl Stream.
Get ARN
To get the Worker role ARN for a Workspace, in the sidebar, select Workspace. In the Stream Worker Group Details section, select a Worker Group and copy the value of the Trust field.
You can use this Worker ARN as the principal in the trust policy for an AWS account IAM role that Cribl Workers will assume. Attaching this trust relationship enables the AssumeRole action, providing cross-account access. For usage details, see the AWS Cross-Account Data Collection topic, Account B Configuration section.
This option applies only to AWS-based Cloud Workers. You cannot use this technique to enable access for Azure-based Worker Groups or to customer-managed hybrid Workers.
Set Up ACL
To set up Access Control List (ACL) Rules, in the sidebar, select Workspace and then Access Control List.
ACL Rules (IPv4 CIDR ranges) let you restrict data sent to your data sources. The Rules you define here are global to all Cribl-managed Worker Groups in Cribl.Cloud in the current Workspace. You can set up a maximum of 9 ACL Rules.
The default 0.0.0.0/0 rule (modifiable) imposes no limits.
End a rule with /32 to specify a single IP address, or with /24 to enable a whole CIDR block from x.x.x.0 to x.x.x.255.
Select Save after adding, modifying, or removing rules. Each change takes up to 5 minutes to propagate. During this time, rule editing is temporarily disabled to prevent conflicts. A successful update proceeds silently - you will not see a confirmation message.
- The ACL options apply only to Cribl-managed Workers. You cannot use them to set access rules on customer-managed hybrid Workers.
- If you delete the default
0.0.0.0/0rule and do not configure any other ACL rules, all inbound data to Cribl-managed Worker Groups in this Workspace will be blocked until you add an allow rule.